Turkey Launches National Security Scans Following Critical PHP Vulnerabilities
Following the disclosure of two critical vulnerabilities in the PHP infrastructure, the Turkish Presidency’s Cybersecurity Directorate initiated a nationwide security scan on October 21, 2026, to protect public digital systems. These vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, carry a high CVSS severity score of 9.2, posing potential risks for remote code execution. While authorities confirmed that the e-Government Gateway (e-Devlet) is secure after rigorous testing, the broader national survey aims to identify and remediate potential exposure across various public and private institutions that rely on the widely used PHP programming language.
- The Presidency’s Cybersecurity Directorate launched national scans to identify potential risks caused by two critical PHP vulnerabilities.
- Security experts confirmed that the e-Government Gateway remains unaffected following comprehensive system checks.
- Official advisories mandate that organizations review their software infrastructure and apply necessary security updates immediately.
Critical PHP Vulnerabilities Threaten Global Digital Systems
Modern internet services rely on complex layers of software, with PHP serving as a fundamental backbone for countless websites, e-commerce platforms, and enterprise portals. The announcement of vulnerabilities with a 9.2 severity rating highlights the inherent risks of modern web development. Because these flaws allow attackers to execute arbitrary code remotely without authentication, the potential for data breaches and service disruption remains significant if patches are not applied.
It is important to note that a vulnerability rating alone does not equate to a successful breach. However, it indicates a severe weakness that requires immediate technical scrutiny. Organizations must assess whether their specific server configurations and PHP versions fall within the vulnerable range to mitigate the risk effectively.
National Security Agencies Prioritize System Integrity
The decision by the Turkish Presidency to initiate national scans underscores a proactive stance toward cyber defense. By issuing formal notifications to relevant institutions, the government ensures that both state-run and independent systems are scrutinized for potential exposure. Because institutional infrastructures often rely on a mix of internal and third-party software, maintaining a comprehensive inventory of utilized components is essential for identifying hidden risks.
The current challenge involves determining the exact scale of the impact. While no public data currently discloses the total number of affected systems, the ongoing efforts signify a robust attempt to standardize security protocols across the public sector. Transparency regarding the results of these scans will be vital in maintaining public trust in digital infrastructure.
Academic Environments Foster Future Cybersecurity Expertise
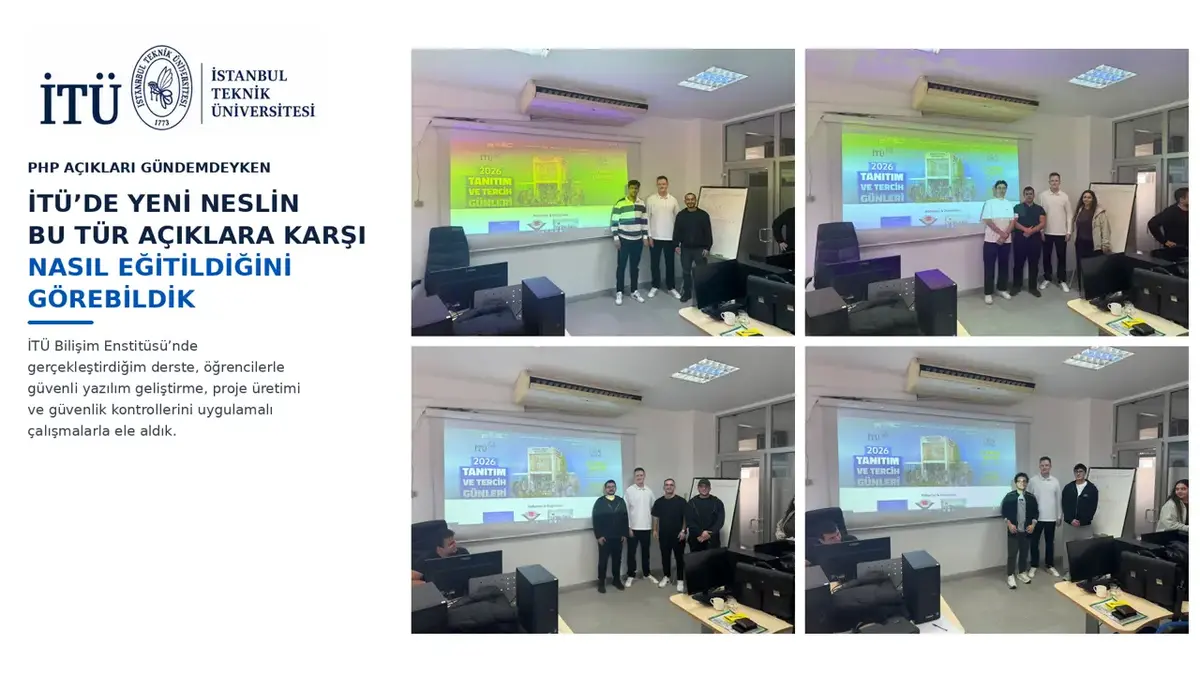
In the wake of these security alerts, practical education in secure software development has become more critical than ever. Recent workshops at the Istanbul Technical University (ITU) Informatics Institute demonstrated that training students to identify and report vulnerabilities is as important as teaching them to write code. By participating in hackathons and security testing exercises, the next generation of developers is learning to treat security as a foundational requirement rather than an afterthought.
These educational initiatives focus on teaching students to evaluate software components, utilize industry-standard resources like OWASP, and perform rigorous testing. This approach ensures that future professionals are prepared to navigate the complexities of real-world threats, where software reliability is paramount to national security.
Proactive Security Measures Prevent Future Breaches
Organizations must move beyond simple patching to ensure comprehensive protection. A complete security strategy includes verifying that the correct updates are applied, auditing system logs for signs of past unauthorized activity, and ensuring that all third-party dependencies are accounted for. Since a patch cannot undo a breach that has already occurred, thorough forensic analysis remains a necessary component of the remediation process.
How do you assess the readiness of your own organization’s digital infrastructure when faced with sudden security threats like these PHP vulnerabilities? Share your thoughts and experiences regarding cybersecurity measures in the comments section below.
Your comment has been submitted,
it will be published after approval.