Trump Mobile Subscribers Exposed in Massive Data Breach
The controversial smartphone brand Trump Mobile is currently grappling with a severe security crisis following the leak of personal data belonging to 3,615 of its subscribers. A cybercriminal group identifying as BYOD announced the release of this sensitive information on the dark web, claiming that the leak encompasses nearly the entire active user base of the company. The breach has compromised critical details including full names, email addresses, phone numbers, and home addresses for thousands of individuals, significantly impacting high-ranking corporate executives associated with the organization. This incident marks a major escalation in the ongoing challenges faced by the brand, which has already been under fire for hardware performance issues and pricing concerns.
- A threat actor group published 3,615 unique subscriber records on the dark web.
- The security breach originated from a Remote Access Trojan infection within the infrastructure of a partner firm, Liberty Mobile.
- Exposed subscriber data included the private contact information of Trump Organization Vice President Eric Brunnett.
The Breach Originated Through a Third-Party Partner System
Cybersecurity experts investigating the incident have determined that the attackers did not breach the primary Trump Mobile servers directly. Instead, the hackers exploited a vulnerability within the infrastructure of an MVNO partner, Liberty Mobile. An employee at the partner company reportedly fell victim to a Remote Access Trojan (RAT), which provided the attackers with an entry point into the corporate network. This unauthorized access allowed the hackers to traverse the system and eventually extract sensitive data from the subscriber database. The incident serves as a stark reminder of the security risks that third-party vendors and external business partners can introduce to larger organizations.
Sensitive Personal Information Was Exposed Publicly
The leaked files contain a comprehensive collection of user data, ranging from order histories and plan cancellation logs to direct contact details. While initial reports suggest that specific records related to T1 phone orders remain secure, the exposure of general subscriber information has triggered significant alarm among the user community. The gravity of the situation is further highlighted by the fact that the database included the private details of Eric Brunnett, a prominent Vice President at the Trump Organization. This inclusion confirms that the breach successfully reached the highest levels of the company’s internal network.
The Brand Faces Ongoing Operational Difficulties
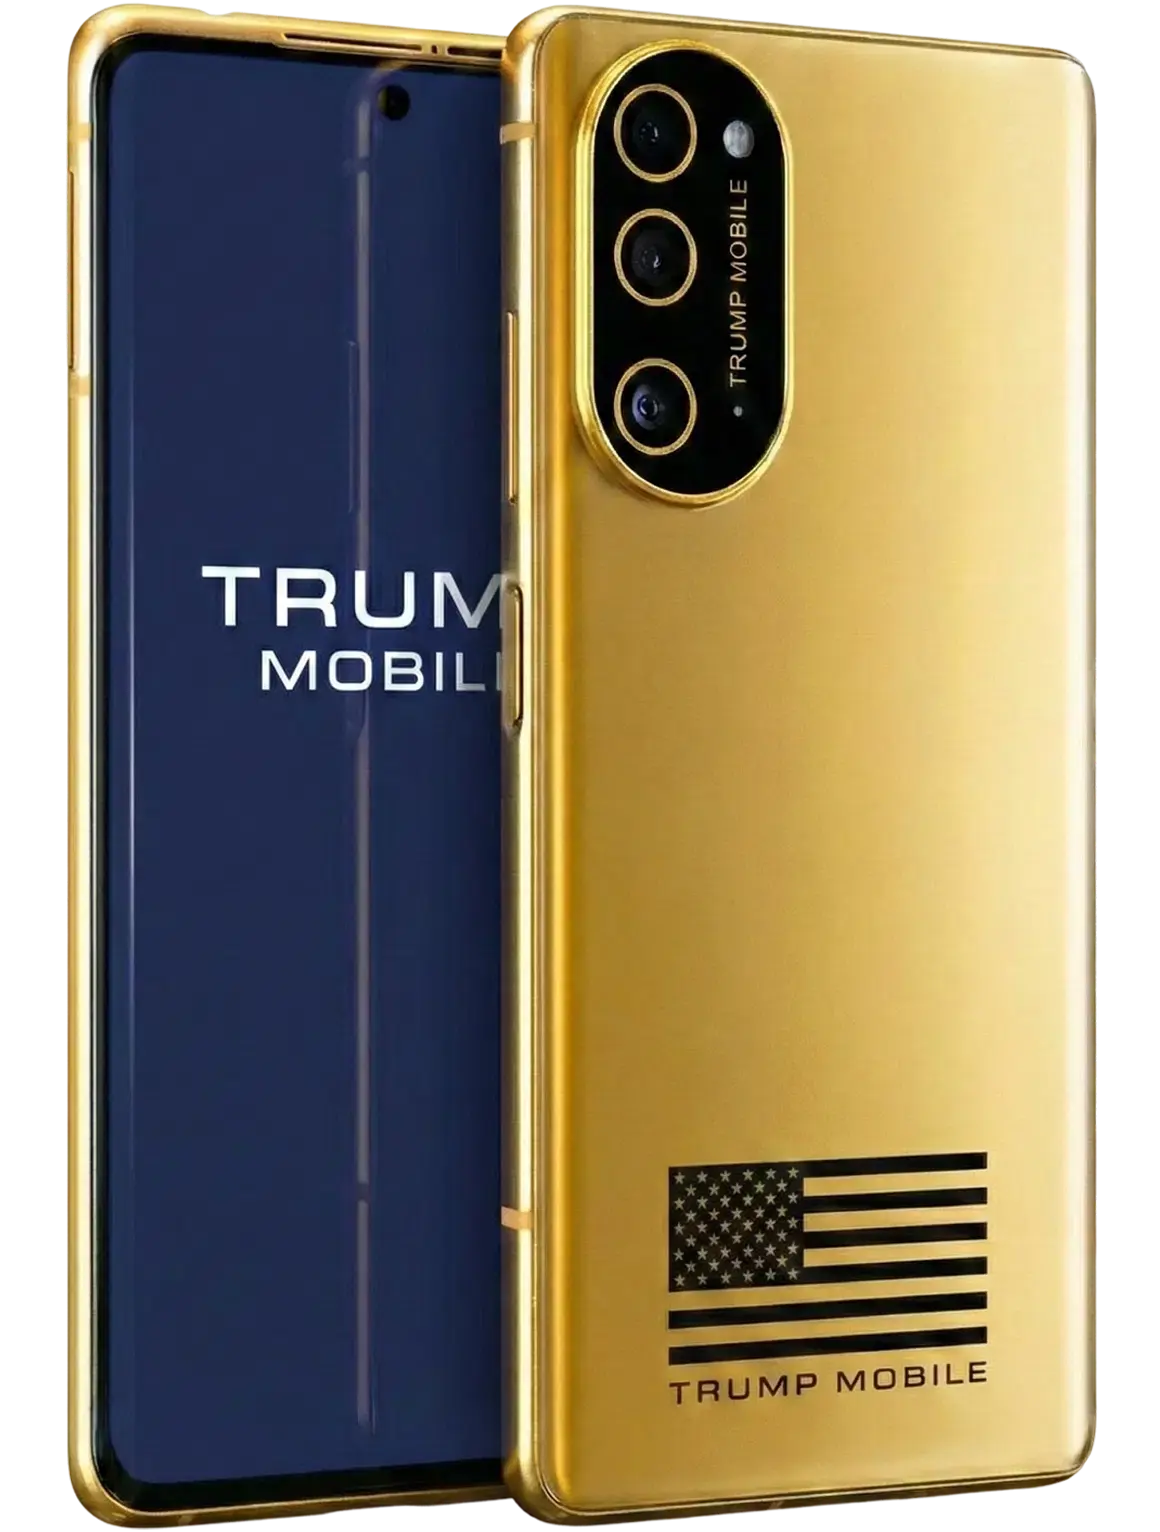
This data security failure arrives at a difficult time for Trump Mobile, as the company has struggled to maintain market confidence. The brand previously faced intense criticism regarding the hardware capabilities and premium pricing of its T1 smartphone series. Additionally, reports of shipping delays and unsatisfactory user experiences have already hampered the company’s reputation. This latest security incident complicates the firm’s efforts to retain its existing customer base and restore public trust. Industry observers are now closely monitoring how the company plans to address the concerns of affected subscribers and whether it will implement more robust cybersecurity protocols to prevent future incidents.
In your opinion, are companies conducting sufficient security audits on their third-party business partners? Please share your thoughts in the comments section on what steps users should take to protect their personal information following such large-scale data breaches.
Your comment has been submitted,
it will be published after approval.