New P7 DarkSword Spyware Threatens Vulnerable iPhone Devices
A sophisticated new variant of the DarkSword spyware, identified as P7 DarkSword, has emerged as a significant threat to iPhone users who have not updated their devices to the latest security patches. Discovered by cybersecurity firm iVerify, this malicious software specifically targets devices with outdated iOS versions, allowing attackers to infiltrate systems and exfiltrate sensitive personal data. The threat actor, which has previously conducted campaigns in countries such as Turkey, Saudi Arabia, and Ukraine, uses this evolved malware to perform remote command execution, granting unauthorized access to everything from saved passwords to cryptocurrency wallet assets.
- The P7 DarkSword malware facilitates remote command execution and exfiltration of sensitive data from compromised iPhone devices.
- The spyware integrates into the iOS SpringBoard process to maintain persistent communication with command and control servers.
- Apple has released critical security updates, including iOS 15.8.7 and 18.7.7, to patch the vulnerabilities exploited by the attack chain.
Technical Capabilities Are Being Enhanced by Attackers
The naming convention for P7 DarkSword stems from the p7_ variable prefix identified in the modified source code. Security researchers have observed that this iteration of the malware is more stable and leaves fewer forensic traces than its predecessors. By utilizing the Coruna exploit chain alongside vulnerabilities in legacy iOS versions, the attackers successfully bypass standard security mechanisms to deploy additional malicious payloads. 
A notable evolution in this version involves the extraction of data from the device’s Keychain. The software automates the process by converting stolen data into JSON format directly on the phone before transmitting it to external servers. Furthermore, the malware features specialized functions designed to target specific applications, such as the imToken cryptocurrency wallet, demonstrating a highly focused approach to financial theft.
Command and Control Mechanisms Are Operating Constantly
P7 DarkSword maintains a sophisticated connection with attacker infrastructure by embedding itself into the SpringBoard, which is the core system process responsible for the iOS interface. This allows the spyware to operate in the background with a high degree of stealth.  The malware checks for new instructions from the command and control servers every 15 seconds, a frequency that can be adjusted remotely by the operators.
Through these remote commands, attackers can browse the file system, access the Apple Notes database, and export personal photographs. The ability to modify the connection interval ensures that the spyware remains responsive to the attackers’ real-time requirements while evading traditional detection methods.
Security Updates Are Required for Protection
It is important to note that the emergence of P7 DarkSword does not necessarily imply the discovery of a new zero-day vulnerability. Instead, it represents a refinement of the malware payload that exploits already known security gaps. Apple has proactively released updates including iOS 15.8.7, 16.7.15, and 18.7.7 to address the specific vulnerabilities used in the DarkSword attack chain. 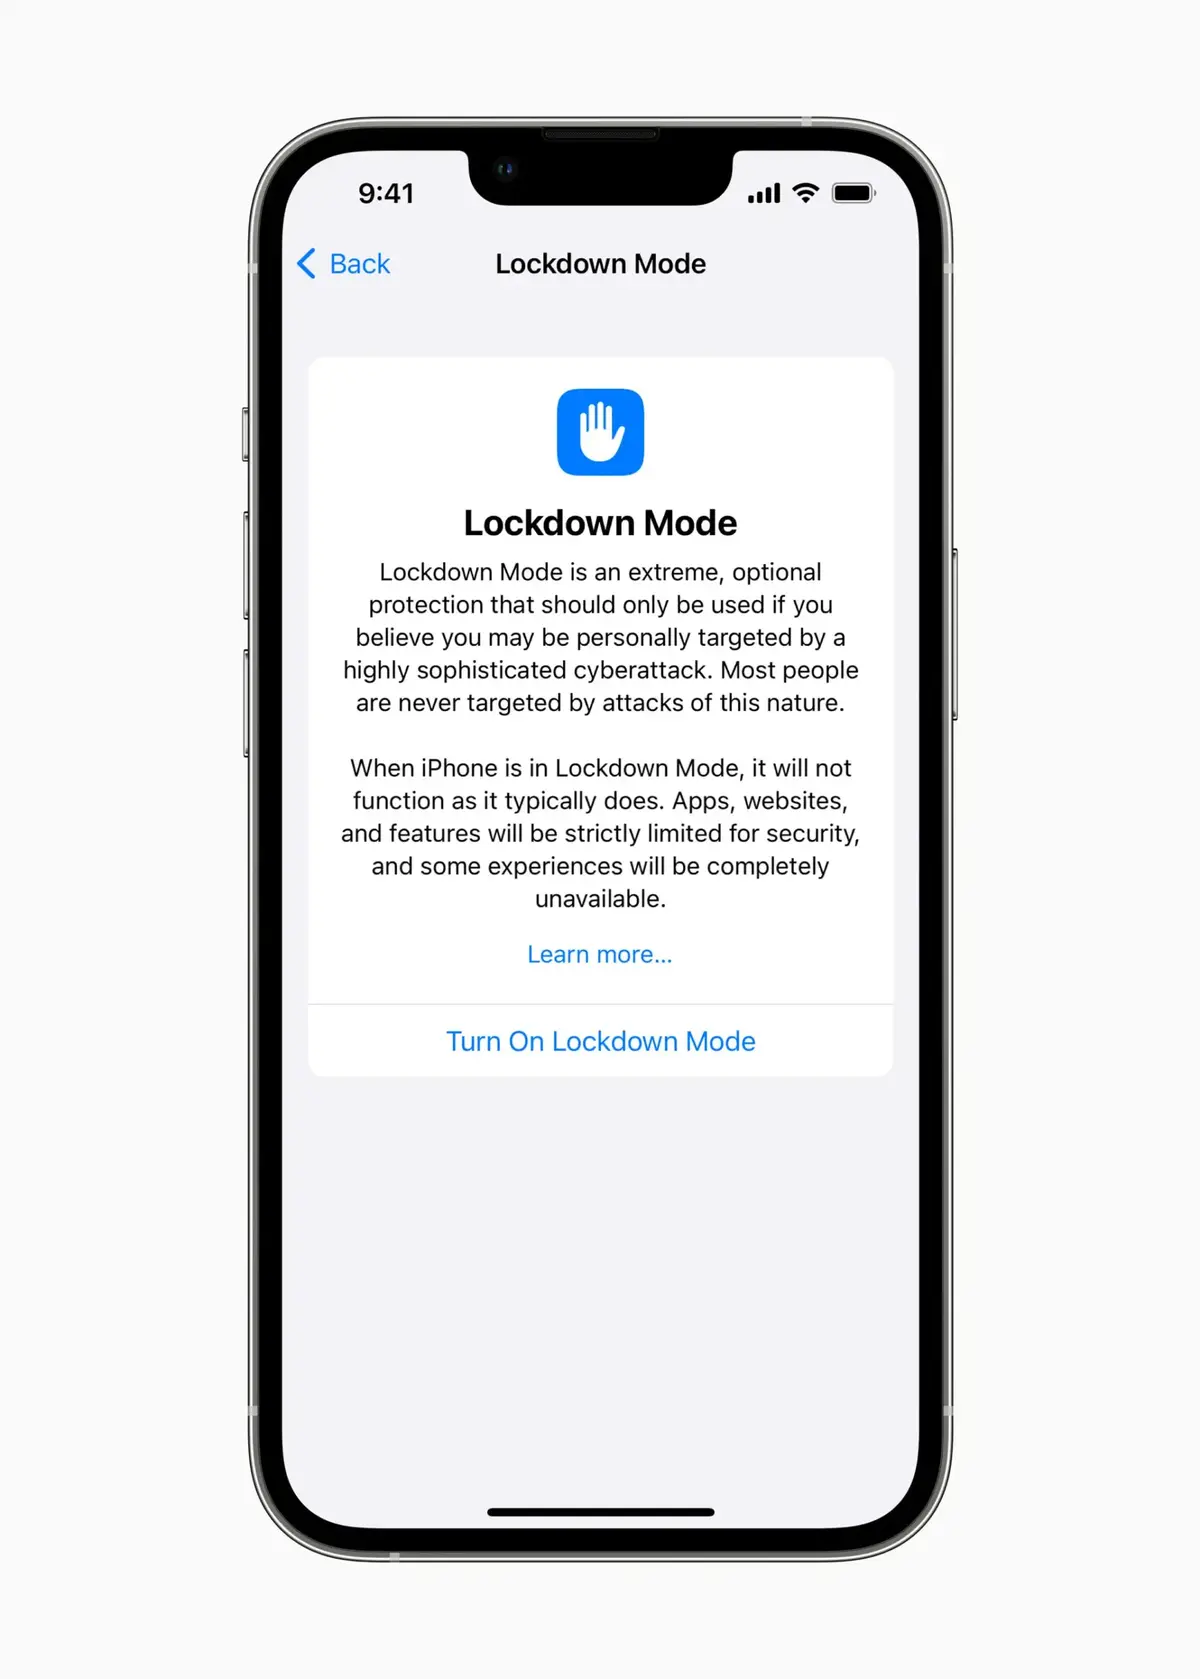
Users are strongly advised to update their devices immediately to ensure these security patches are applied. For individuals who believe they are at a higher risk of targeted attacks, enabling Lockdown Mode in the iOS Privacy and Security settings provides an additional layer of defense by limiting system functionality that attackers often exploit. The technical modifications made by the developers of P7 DarkSword have rendered some previous detection indicators ineffective, making system updates the most reliable defense.
Given the increasing sophistication of mobile spyware, what security measures do you prioritize to keep your personal information safe on your smartphone? Share your thoughts and experiences in the comments section below.
Your comment has been submitted,
it will be published after approval.