National PHP Security Alert Issued Amid Critical Vulnerability Risks
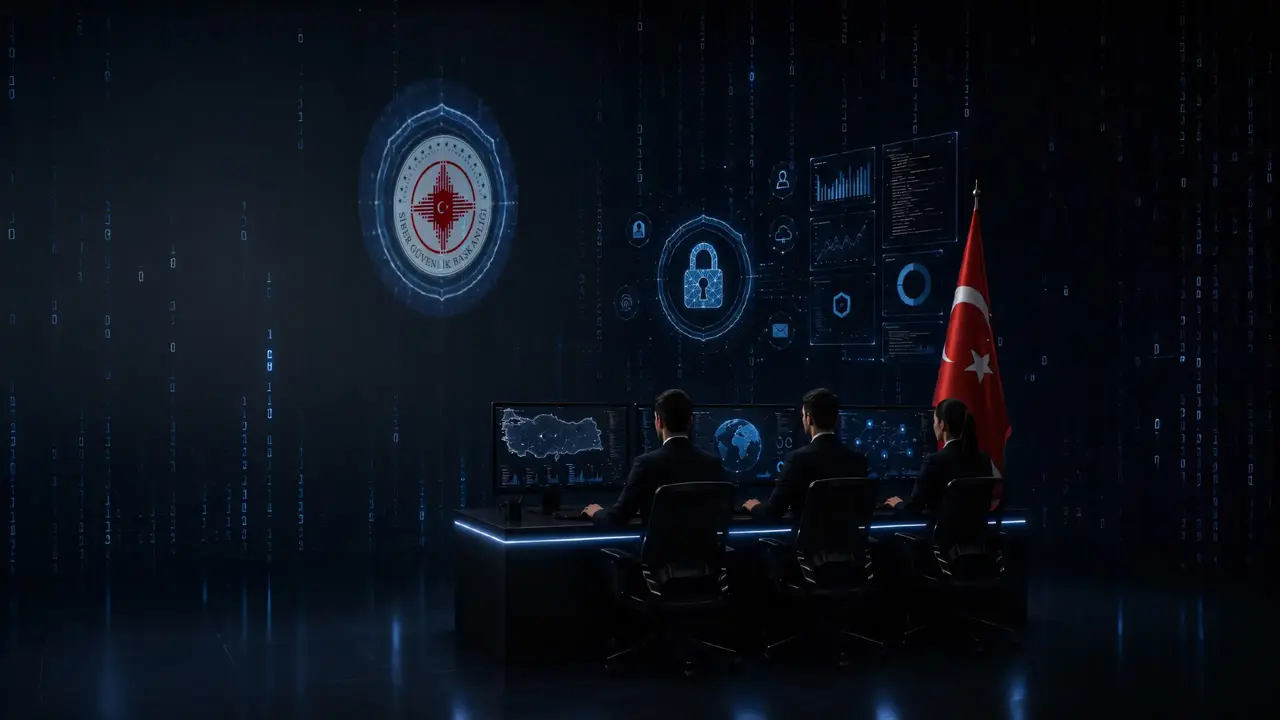
A critical security vulnerability known as “PHP2Shell” has been identified within the PHP infrastructure, prompting the Presidency of the Republic of Turkey Cyber Security Directorate to issue a nationwide alert. This vulnerability poses a severe threat to countless websites and corporate applications globally, potentially allowing unauthorized actors to execute remote commands without requiring credentials. In response to the discovery of these two major flaws, the national cybersecurity authority has launched comprehensive system scans and protective measures. Meanwhile, officials have confirmed that the e-Devlet (e-Government) Gateway, which serves over 69 million users, remains secure and fully operational after undergoing rigorous technical inspections.
- The PHP2Shell vulnerability enables unauthorized remote command execution without requiring user credentials.
- The Turkish Cyber Security Directorate has initiated nationwide scans to mitigate potential system compromises.
- The e-Devlet infrastructure remains unaffected due to its robust, distributed security architecture.
- Authorities have instructed all public and private entities to install mandatory security patches immediately.
PHP2Shell Threat Allows Unauthorized System Access
The newly discovered PHP2Shell threat represents a significant escalation in web infrastructure risks. By exploiting these flaws, malicious actors can bypass traditional authentication mechanisms, effectively gaining control over vulnerable servers without needing a valid username or password. This capability creates a dangerous window for attackers to install malware, steal sensitive data, or disrupt service availability.
The Cyber Security Directorate is currently managing the national response by coordinating real-time security scans across critical infrastructure. Experts warn that the widespread usage of PHP as the backbone of modern web development makes this a high-priority concern for all IT administrators and system architects.
Public and Private Sectors Must Apply Updates
To combat this threat effectively, the Directorate has issued an urgent directive to both public institutions and private sector stakeholders. The primary focus of this guidance is to minimize the attack surface by ensuring all software environments are properly hardened. Organizations are required to conduct an immediate audit of their PHP versions to identify any outdated or unsupported components that may be prone to exploitation.
Furthermore, the official advisory emphasizes that simply identifying the vulnerability is not enough. System administrators must prioritize the installation of the latest security patches provided by software developers. Any components that have reached their end-of-life cycle must be isolated or completely removed from production environments to prevent future security breaches. Maintaining a strict patch management schedule is essential for the longevity and integrity of digital services.
e-Devlet Gateway Maintains Secure Operations
Despite the global concern surrounding PHP2Shell, Turkey’s e-Devlet Gateway continues to function without interruption. The platform utilizes a sophisticated, distributed architecture that avoids storing data in a single central repository. Instead, it relies on secure, encrypted tunnels that facilitate communication between various public institutions.
Rigorous testing performed by specialized security teams has confirmed that the platform’s current security posture is sufficient to withstand the identified PHP vulnerabilities. Digital public services remain under 24/7 monitoring by specialized incident response teams, ensuring compliance with international information security standards. The government continues to provide technical guidance to help other entities align their systems with these high-security parameters.
Have you checked your own web servers or corporate infrastructure for these specific PHP vulnerabilities yet? Share your experiences with security updates and let us know what steps your organization is taking to stay protected in the comments section below.
Your comment has been submitted,
it will be published after approval.